
With fewer than 100 Chinese characters, a hacker unleashed an army of artificial intelligence agents that spent hours searching for vulnerabilities and breaking into corporate websites, carrying out almost the entire operation without human intervention. The result was a series of intrusions affecting websites belonging to more than 100 companies, including John Deere, SharkNinja and Cummins, according to a Reuters investigation published Monday.
The operation illustrates how AI is changing the economics of cybercrime. A single attacker can now automate work that previously required considerable technical expertise and time, potentially targeting hundreds of organizations while spending relatively little money.
Gallery
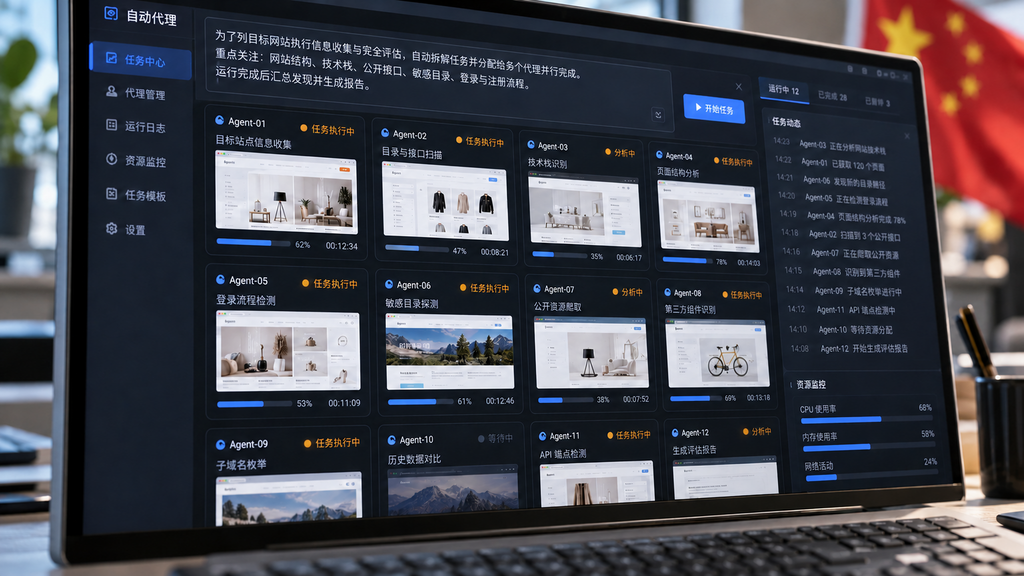
An AI-generated illustration of a hacker using autonomous agents to target corporate websites
(Illustration: Created with ChatGPT)
The activity was uncovered by Snorre Fagerland, principal threat researcher at cybersecurity company NorForge, who tracked AI agents as they scanned websites, identified weaknesses and attempted to exploit them. According to Fagerland, the hacker delegated almost every stage of the operation to AI, from the initial reconnaissance to the intrusions themselves.
Reuters independently identified some of the affected companies by examining records of the attacker's activity. However, the news agency could not determine how many of the breaches resulted in the unauthorized extraction of sensitive information.
The hacker used Cairn, an open-source AI problem-solving platform that allows autonomous agents to operate tools, evaluate the results and decide what actions to take next. Although the platform was not developed specifically for cyberattacks, its capabilities can be exploited to identify security vulnerabilities and attempt to gain unauthorized access to systems.
The campaign involved more than 1,200 attempted intrusions, primarily targeting e-commerce websites in the U.S., Canada, Australia and Japan. Successful breaches typically required around 23 hours of automated probing and testing.
Fagerland estimated that the operation consumed approximately $5,000 worth of AI model usage, equivalent to roughly $50 for each successful intrusion. The relatively low cost highlights how AI tools could make large-scale cyberattacks accessible to individual attackers rather than only well-funded criminal organizations.
The agents also demonstrated an ability to adapt when their initial attempts failed. In one case described by Fagerland, after failing to identify a vulnerability in a company's main application, the agents investigated associated infrastructure and discovered a publicly accessible administration interface. They subsequently identified another weakness and reported exploiting it to execute unauthorized commands on the server.
Fagerland said the techniques went beyond the capabilities typically associated with inexperienced hackers using ready-made attack tools. The AI systems were able to pursue alternative approaches and continue working through problems without constant direction from their human operator.
Dario Amodei and Sam Altman, leaders of two of the world's major AI companies
(Photo: Reuters)
Some of the instructions issued to the agents were remarkably direct, including requests to obtain credit card information or cryptocurrency. The operator also sought to maintain access to commercial and payment systems, potentially allowing the intrusions to be exploited for financial gain later.
The researcher's ability to follow the campaign came from an unexpected source: The attackers had left some of their own systems exposed to the internet. Beginning around October 2, Fagerland identified approximately two dozen Cairn installations being used for malicious activity, allowing him to observe the agents' operations.
The Chinese-speaking hacker responsible for targeting more than 100 company websites was the most prolific operator identified. But other users of the platform were also engaged in malicious activity. Fagerland documented one attacker stealing credit card information and another attempting to use AI agents to steal from a cryptocurrency exchange. Those activities were separate from the main hacking campaign.
Despite the scale of the reported intrusions, several affected companies described the impact as limited or said they were still investigating. An intrusion into a support website or a third-party service does not necessarily mean that attackers gained access to a company's main systems or customer databases.
John Deere said it had taken corrective action following the incident and had no indication that sensitive information had been accessed.
SharkNinja said the affected website was a separate platform containing product support information, rather than sensitive customer or corporate data, and that the threat had been contained.
Cummins, meanwhile, said it was investigating a report of a possible cyberattack involving a website operated by one of its external suppliers.
Reuters also identified additional companies through its examination of the attack records, although the available evidence did not establish the full extent of any information stolen.
Even a breach limited to a secondary corporate website can present security risks. Attackers who gain control of such sites may be able to alter content, redirect visitors to fraudulent pages or exploit a trusted company's name to distribute malicious files. There is no evidence in the report that these activities occurred in the cases involving the three major companies.
The broader concern is what the operation demonstrates about the changing balance between attackers and defenders. AI agents can work continuously, test multiple approaches and pursue numerous targets without requiring a human hacker to supervise every step.
Yuval Itzchakov, co-founder and CTO of cybersecurity company A Security, said the incident illustrates the growing threat posed by autonomous AI tools.
"This is another example of how AI is lowering the bar for threat actors, making attacks both faster and more sophisticated. The only way for organizations to prepare for this reality is to use the same AI capabilities to evaluate their environments before attackers do."
For companies, that means even systems previously considered too obscure or time-consuming to attract sophisticated attackers could face growing risks. And for cybercriminals, the combination of inexpensive AI models and autonomous tools is removing some of the technical and financial barriers that once limited large-scale hacking.
The full consequences of this particular campaign remain unclear. But its central warning is difficult to ignore: A single individual, armed with a few instructions and several thousand dollars, can now direct AI systems to carry out a hacking operation spanning more than a thousand potential targets.